Only you can build your product. The proof it’s safe — that’s ours.
Comp AI is your compliance team. We do the work. You approve it.
Certified on the date your deal depends on.
- SOC 2
- ISO 27001
- HIPAA
- GDPR
Three questions. No email needed to see it.
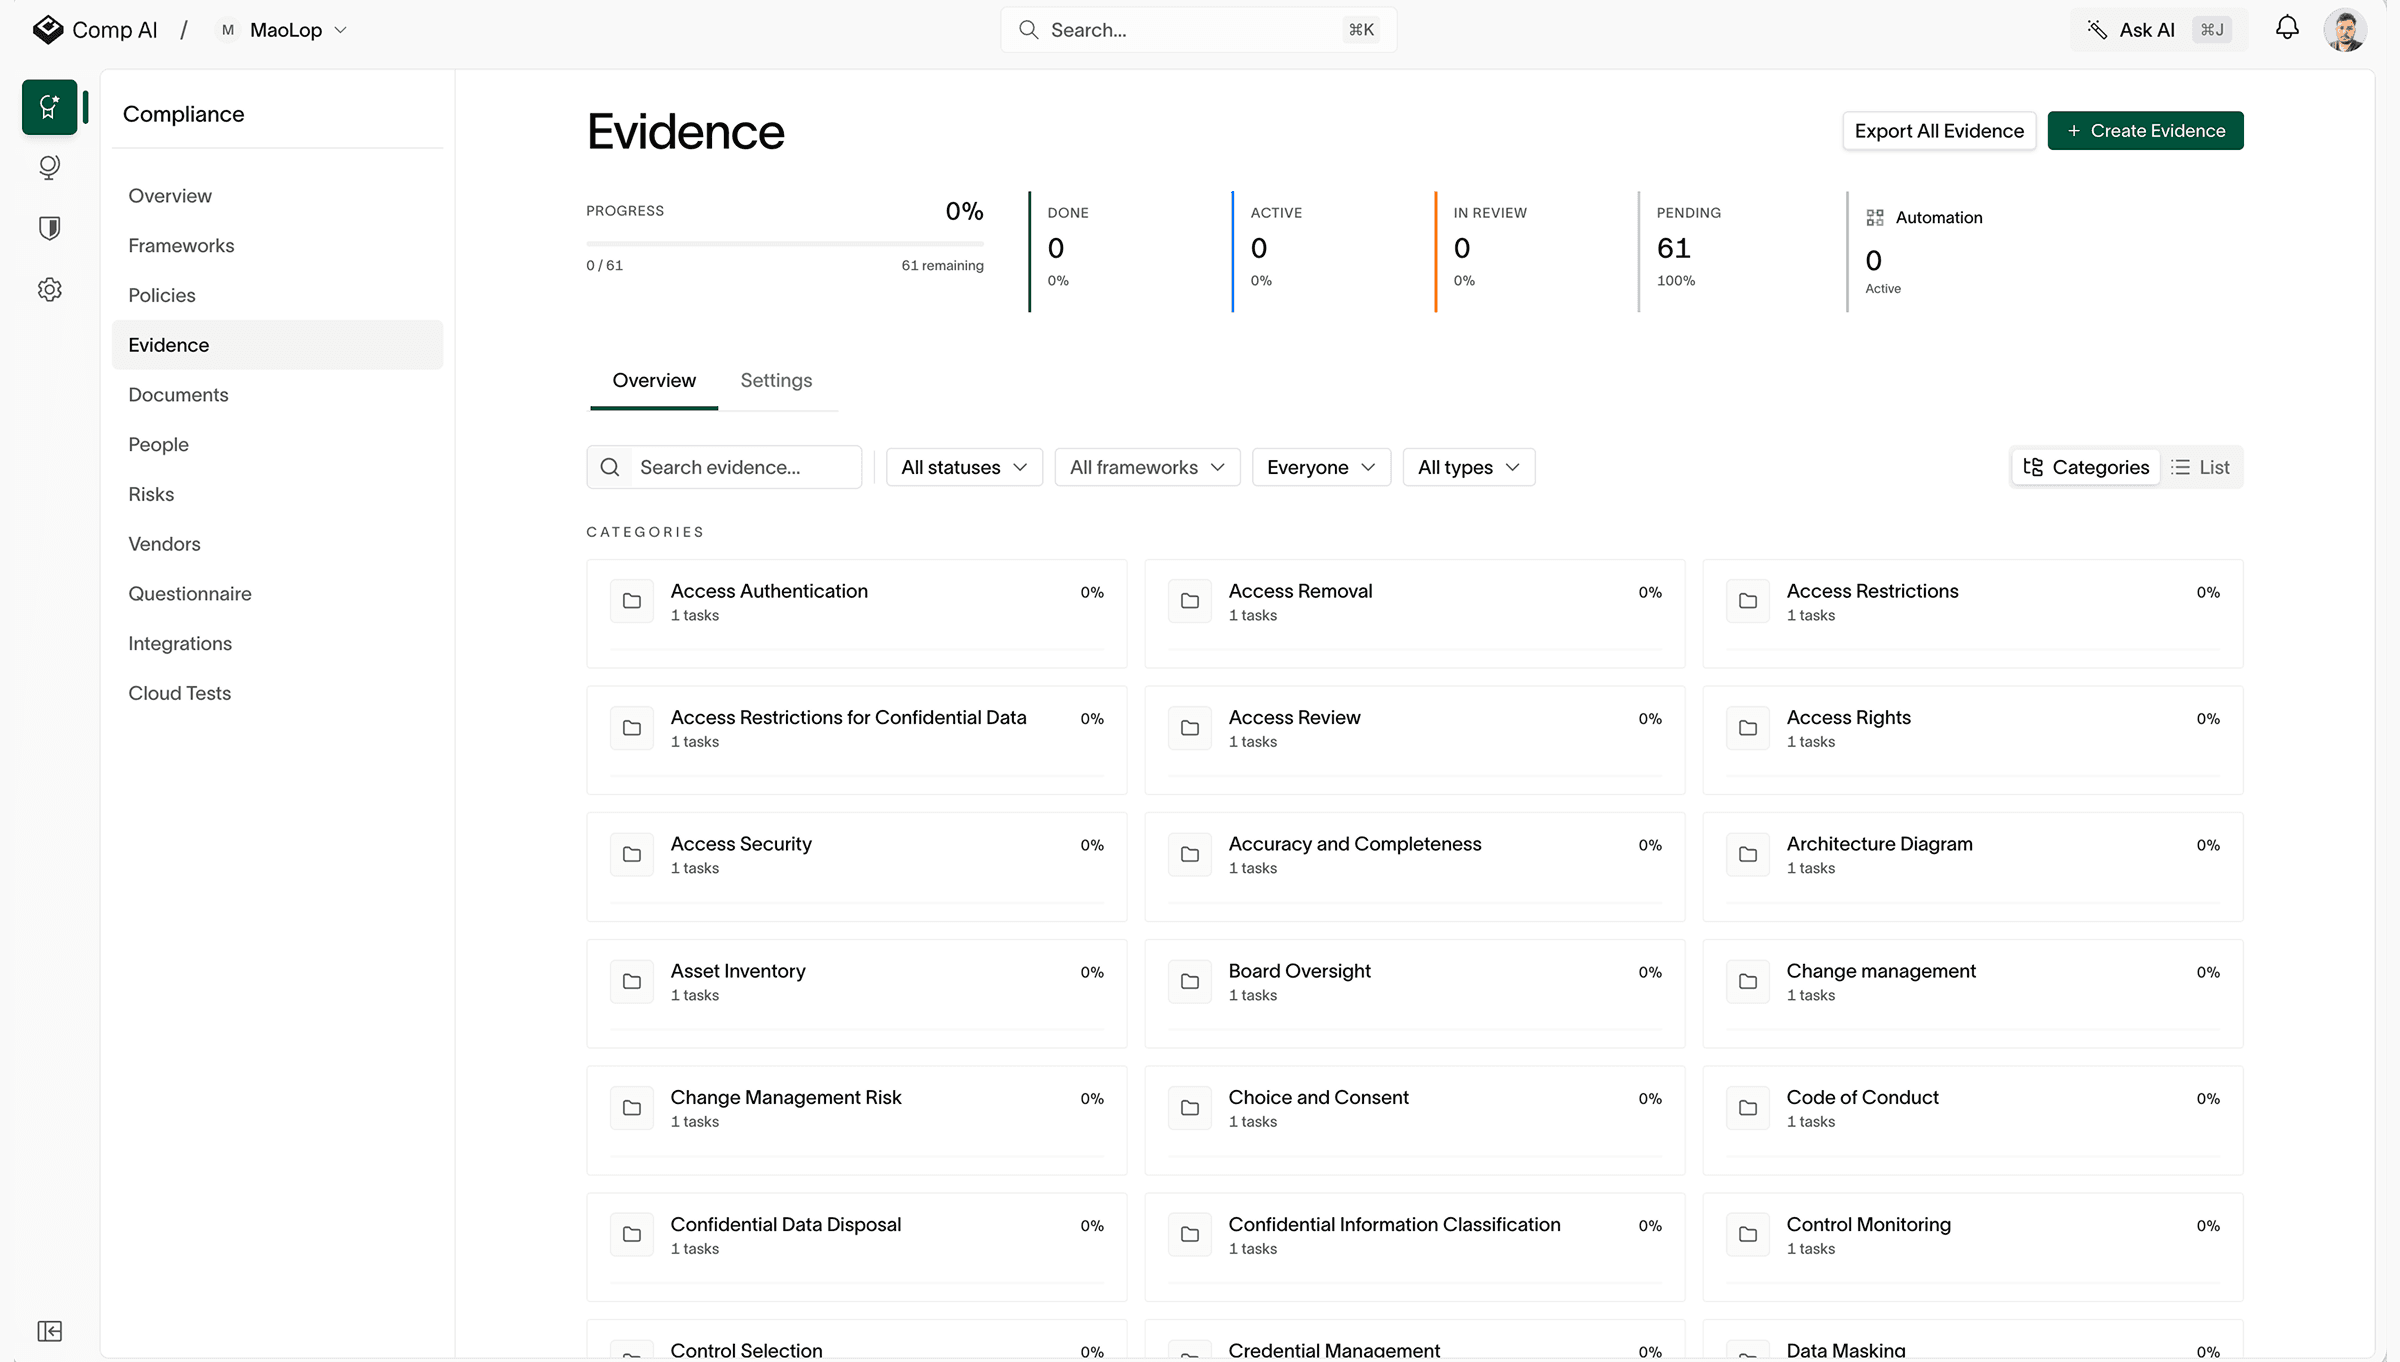
Trusted by 1,000+ teams
Weeks, not quarters.
Every company below agreed to be named.
20 days
Audit-ready. First large customer signed.
< 2 weeks
Ready to start observation after switching platform.
3 frameworks
SOC 2, ISO 27001 and GDPR as one programme.
The reason it is weeks: 580+ integrations pull the evidence straight from your own systems, mapped to controls as it arrives. The hours left over are the decisions only you can make.
Want your timeline?
When someone asks for proof, you send a link.
Your Trust Center is a live page of your security posture — frameworks, policies, controls, daily checks — updated as your systems change. No PDFs, no back-and-forth. Always the current truth.
- 5
- frameworks
- 27
- policies
- 44
- controls
- 6
- subprocessors
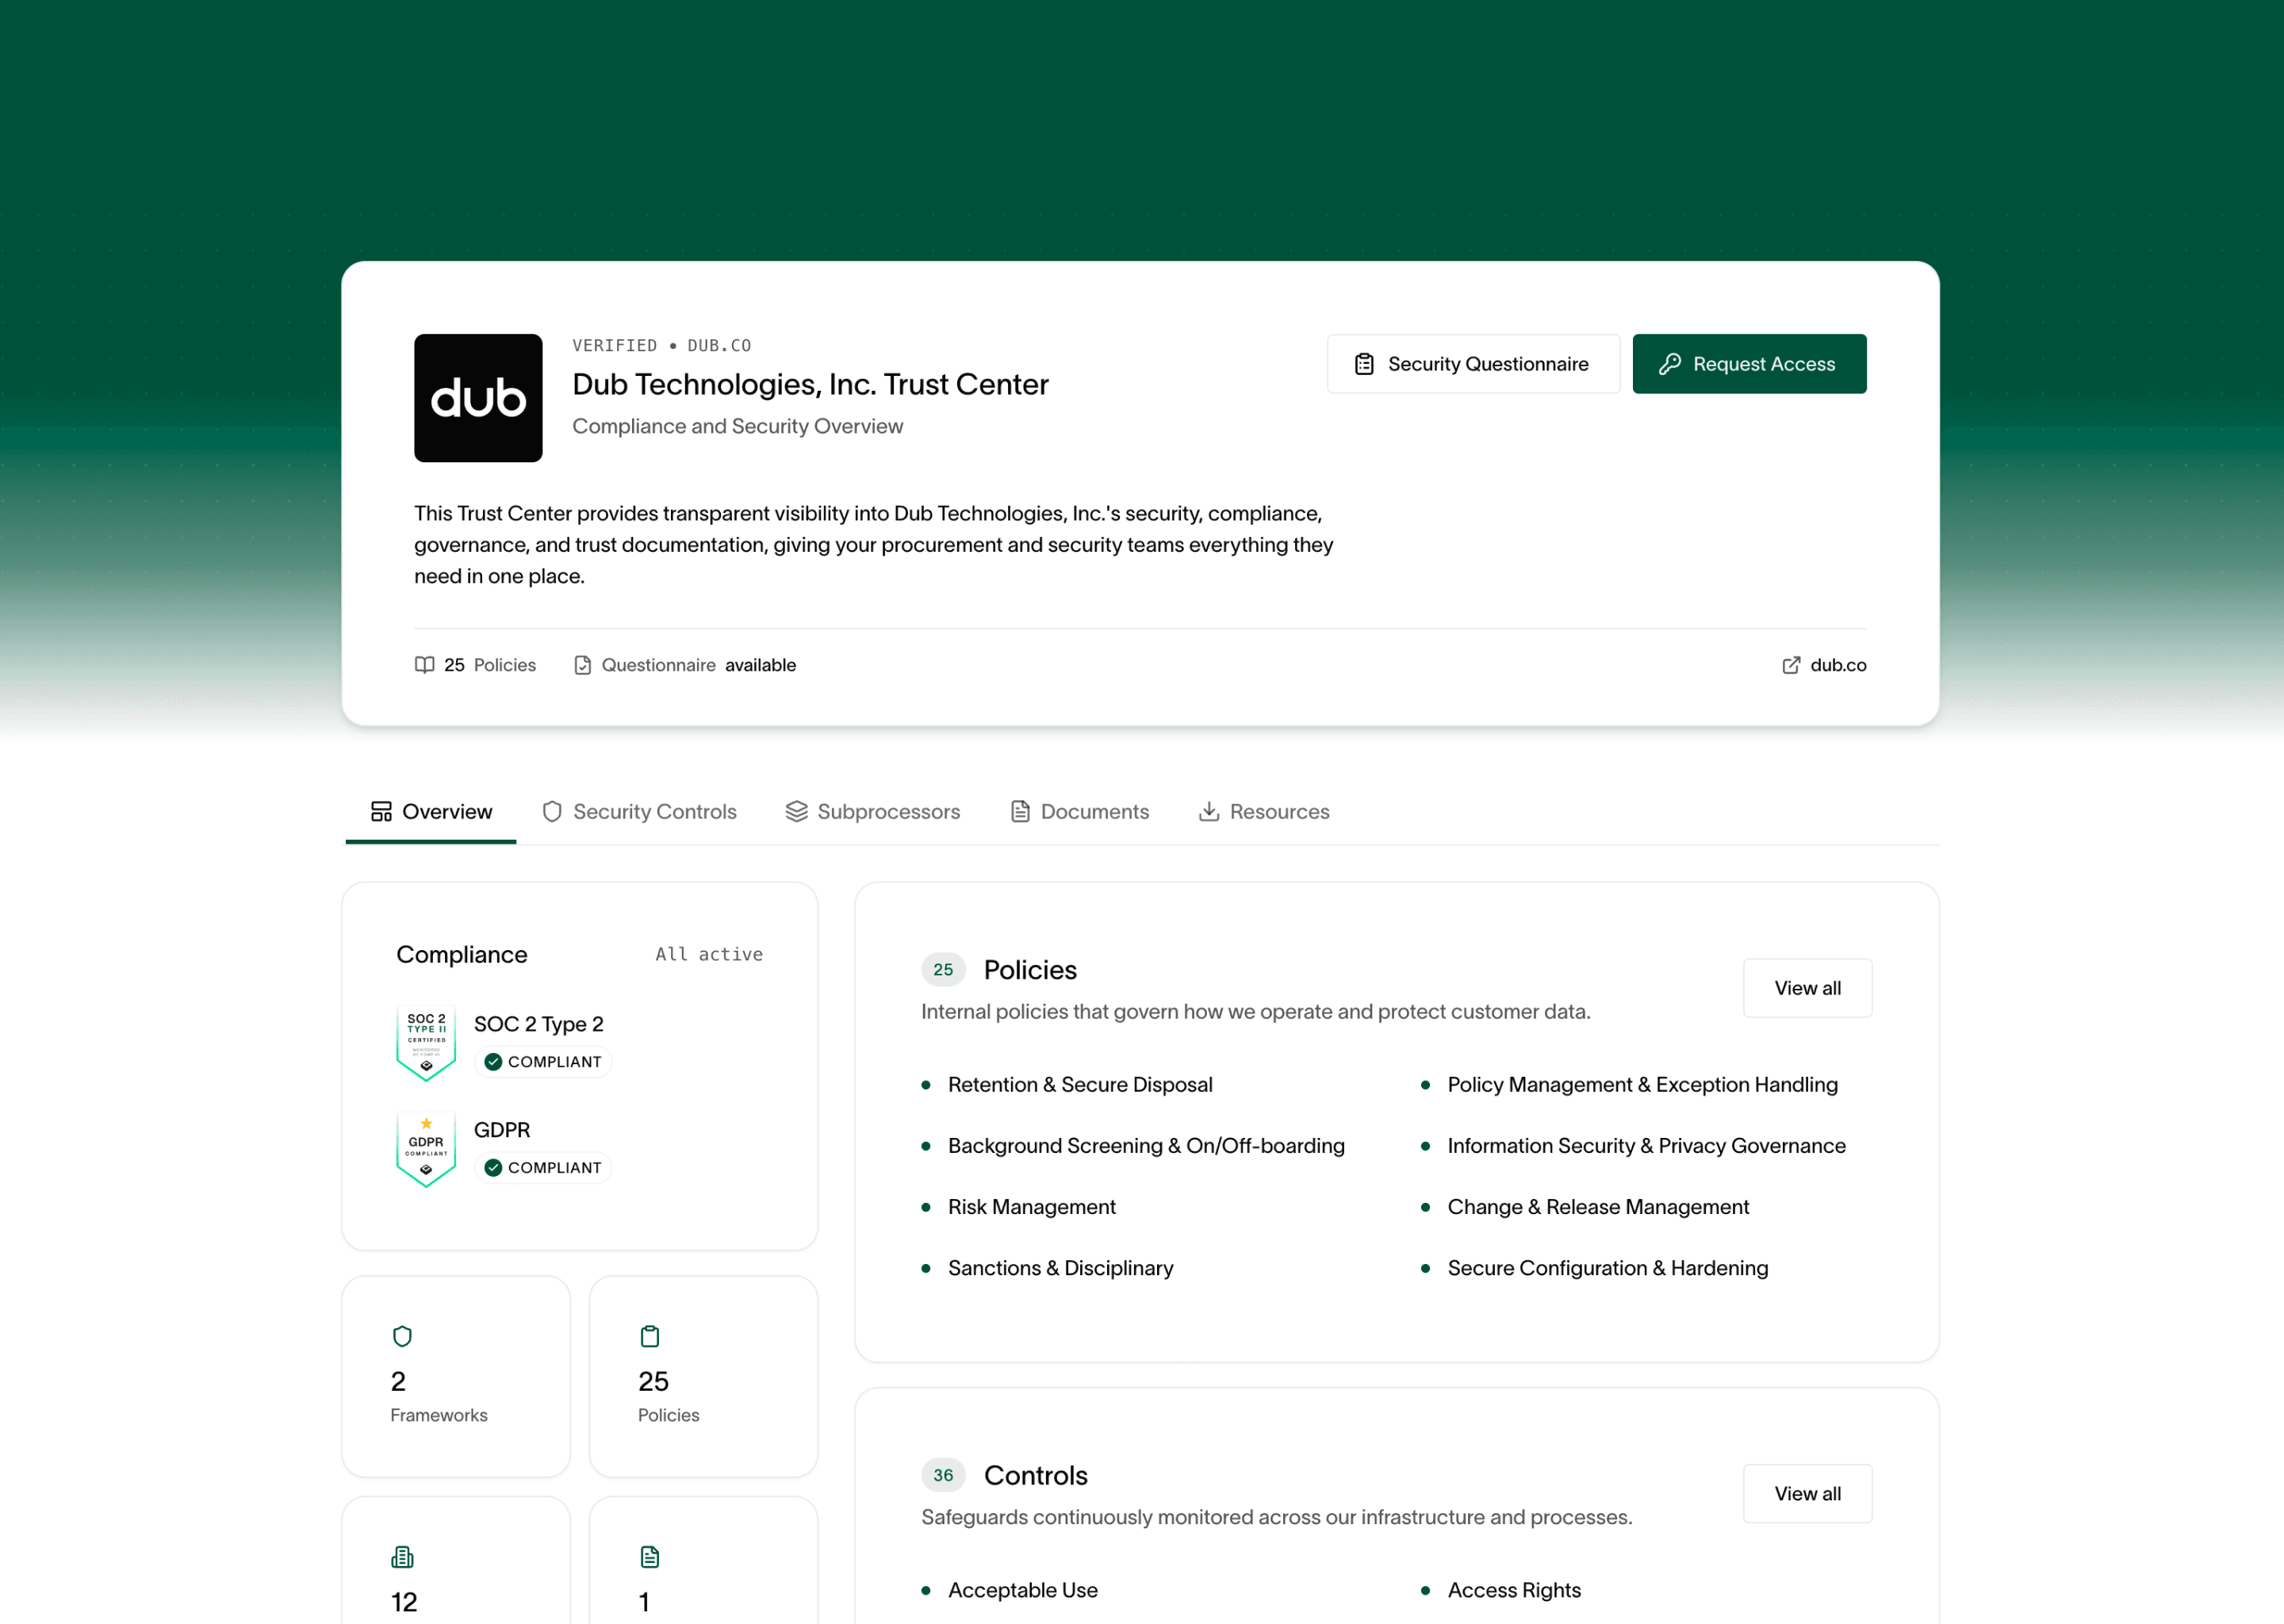
Everything behind it, verified continuously
Access review completed across 12 systems
Disk encryption verified on every device
SOC 2 evidence refreshed from AWS
Vendor DPA signed and filed
New subprocessor published to your Trust Center
Firewall check passed on every laptop
Information Security policy approved
TLS certificate renewed before expiry
A buyer opened your Trust Center
Risk assessment drafted for a new vendor
Daily cloud scan found no misconfigurations
ISO 27001 control mapped automatically
Security questionnaire answered from your program
Screen lock enforced on 3 new devices
GDPR records of processing updated
Penetration test report generated
Antivirus active on every machine
Offboarding revoked access in 6 systems
Evidence pulled from 580+ integrations
Draft policy hidden from your Trust Center
HIPAA safeguards verified
Vendor risk score changed — flagged for review
Encryption at rest confirmed on every data store
Password length verified on all accounts
Change management approval logged
Trust Center shared with a security team
Control failed — flagged before the audit
SOC 2 Type II observation period started
Auditor invited to your evidence room
Data retention schedule reviewed
New device enrolled — agent installed
Separation of duties verified
Incident response plan acknowledged
Access control policy generated from your stack
Onboarding checklist completed
Cloud monitoring ran its daily scan
Failing control removed from your Trust Center
Framework added — controls mapped across both
All published controls passing
Certified because the work actually happened.
An independent firm audits you
An approved, independent audit firm performs the audit. Not us.
Security testing included
Penetration testing is part of the same programme, not a separate purchase.
Checked every day
Daily scans of your cloud systems, so the certificate is still true in month twelve.
Evidence arrives with its source attached — which system it came from, when it was collected, which control it satisfies.
Why there is no price on this page.
A single price would be too high for a simple programme and too low for a complex one. So here is what we can tell you now, without a call.
What is included
The platform, the audit, and the security testing. One price.
What is added later
Nothing.
What changes your price
How many certificates you need, how many people work at your company, and your deadline.
Getting certified is the easy half.
Documents become old. A rule stops matching how you work. An auditor asks something new. This is the point where most platforms go quiet.
A person, not a ticket
Direct Slack access to our compliance experts. Under three minutes for a reply.
Nothing expires quietly
Daily checks, so problems appear before your customer finds them.
Problems get solved, not logged
When something does not fit your company, a person works it out with you.
If we miss your date, if you fail the audit, or if you lose a customer's security review because of us — you get your money back.
Comp AI was built by three founders who went through this process at their own companies.
Still deciding? Start with the timeline.
The three questions people ask before they book.
- How can this take weeks when it took me months before?
- Because collecting the evidence is the slow part, and that is what is genuinely automated — pulled from your real systems and mapped as it arrives.
- Who does the audit?
- An independent, approved audit firm. Not us.
- What happens if it does not work?
- Miss the date, fail the audit, or lose a customer's security review because of us, and you get your money back.
Three questions, and we’ll show you your timeline.
Or talk to a person instead.